Latest activity
-
GGhostMachine posted the thread iSCSI connection dropping when non iSCSI switch restart in Proxmox VE: Installation and configuration.We are running Proxmox VE 9.2 on 3 HPE G10 servers and a Synology iSCSI storage unit. We run a separate redundant set of switches for the iSCSI connection to the Synology unit, however when we recently performed a firmware update to our core...
-
DDirk_S1 reacted to EllerholdAG's post in the thread Proxmox VE: Are we getting too many kernel updates for an enterprise virtualization platform? with
 Like.
In a proper HA setup kernel updates and restarts can be applied live. I'd rather have more Bugfixes and security enhancement than not. It's rather concerning that other platforms don't have this much updates. Doesn't ESXi have the same security...
-
DDirk_S1 reacted to Neobin's post in the thread Proxmox VE: Are we getting too many kernel updates for an enterprise virtualization platform? with Like.
One complains about too much updates and the next one would complain about bugs and especially vulnerabilities if they were not patched asap. It is obviously way better to have the updates available; if and when you are installing them and reboot...
-
Bbirdy reacted to EllerholdAG's post in the thread Proxmox VE: Are we getting too many kernel updates for an enterprise virtualization platform? with Like.
Youd have to spend an enormous amount of time, tokens or money to research each and every CVE. Does it affect me? Am I vulnerable? Is there an exploit out there? If not now, is there one tomorrow? It's faster and safer to just update and be done...
-
Jjsmags reacted to bbgeek17's post in the thread Not able to access- local gateway, Public DNS- get "Destination Host Unreachable", no PVE GUI with Like.
What happens when you ping host1 from host2? What does "arp -na" on host2 show after the ping presumably fails? Take the cable from host1 and connect it directly to host2 - can they ping each other? Change the IP of host1/bad to a different...
-
VV1p3R replied to the thread VE Startet ständig neu.So bis auf das ich das Netzteil getauscht habe habe ich nun alles gemacht und leider immernoch das selbe Problem. anbei der Log vor dem Neustart:
-
-
Aaderumier replied to the thread inconsistent bridge-nf-call-iptables and resulting issues.if I remember, we need to set it in pve-firewall, because sysctl if apply before iptables bridge modules is loaded by the kernel
-
TTErxleben replied to the thread ESXi-Datastore für Migration nutzen.Hast du die Übung auch mal mit einer externen USB-Platte (sofern passend groß vorhanden) versucht durchzuspielen? 90GB in 3h sind schlaffe 1MB/s. Der Wert liegt knapp über Brieftaubengeschwindigkeit.
-
SSolus replied to the thread Backups keep failing verification.I'm using a container on my TrueNAS computer running PBS. This is backing up to a pool with its own generic dataset for this specific purpose. Permissions should be correct, and since it's only a couple vm's/ct's failing it would seem they are...
-
Ddavidharris replied to the thread Migrating from VMWare ESXi 6.0 to Proxmox 9.2 - works!.Useful data point, but I agree it’s an existence proof rather than a support statement. For anyone else trying this, the exact ESXi 6.0 build and VM hardware version matter more than the “6.0” label; old VM hardware or snapshot chains are common...
-
 bbgeek17 replied to the thread Not able to access- local gateway, Public DNS- get "Destination Host Unreachable", no PVE GUI.What happens when you ping host1 from host2? What does "arp -na" on host2 show after the ping presumably fails? Take the cable from host1 and connect it directly to host2 - can they ping each other? Change the IP of host1/bad to a different...
-
JDanke für die Rückmeldungen! Ich habe mich dafür entschieden doch den weg über die Storage-Migration (ESX-Seite) zu gehen und die VMs auf ein NFS schieben und diese dann per qm disk import zu importieren. Dauert zwar ewig aber ist mir dann doch...
-
JI’d avoid piling antivirus onto the hypervisor. In my experience, the biggest wins came from isolating management and BMC traffic, allowing access only through a VPN, removing public exposure, and testing offline restores regularly. I’d also be...
-
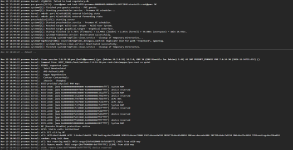
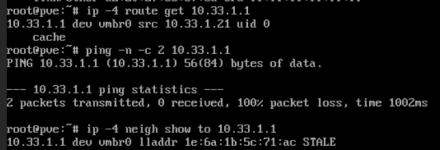
Jjsmags replied to the thread Not able to access- local gateway, Public DNS- get "Destination Host Unreachable", no PVE GUI.Hi, thank you! The text is from a host that works- the screenshots are from the problematic host- where I am only able to connect and take screenshots thru iDRAC. Apologies for the inconvenience!
-
Jjsmags replied to the thread Not able to access- local gateway, Public DNS- get "Destination Host Unreachable", no PVE GUI.Thank you for your kind response, guidance and help! Please see attached results. Thank you! PS. I'm only able to shell into the host using iDRAC- hence not able to take copy of the actual text and hence the screenshots.
-
-
Kkarlsiu1 replied to the thread Security Hardening.I’d avoid piling antivirus onto the hypervisor. In my experience, the biggest wins came from isolating management and BMC traffic, allowing access only through a VPN, removing public exposure, and testing offline restores regularly. I’d also be...
-
CCookiefamily reacted to kalium's post in the thread Ceph 21.2 Umbrella Release Available as test preview and Ceph 19.2 Squid EOL with Like.
Proxmox's build works on x86-64-v2. I'm running it in a cluster with Xeon E5 v2 hosts (PowerEdge R620) without issues so far. IIRC, the requirement of x86-64-v3 is due to Cephadm's container using Rocky Linux 10 as base image.
-
JJohannes S reacted to EllerholdAG's post in the thread Proxmox VE: Are we getting too many kernel updates for an enterprise virtualization platform? with Like.
Youd have to spend an enormous amount of time, tokens or money to research each and every CVE. Does it affect me? Am I vulnerable? Is there an exploit out there? If not now, is there one tomorrow? It's faster and safer to just update and be done...
-
JJohannes S reacted to LnxBil's post in the thread Proxmox VE: Are we getting too many kernel updates for an enterprise virtualization platform? with Like.
Yes, sure ... the problem is also that without a working exploit that is known to the reviewer, you cannot say how critical a fix needs to be applied. Some are very easy to exploit, some very complicated; some are just sending a few crafted...
-
JJohannes S reacted to proxuser77's post in the thread Proxmox VE: Are we getting too many kernel updates for an enterprise virtualization platform? with Like.
Well thanks to AI, exploits for the corresponding vulnerabilities are also being developed much faster. So, critical vulnerabilities should be patched as soon as possible. That's would be a massive amount of work if they wanted to do it...