Latest activity
-
Mmircolino posted the thread cfg80211: failed to load regulatory.db in Proxmox VE: Installation and configuration.Running PVE on an Intel NUC: root@po:~# pveversion pve-manager/9.2.11/f6997e698c7933ea (running kernel: 7.0.14-12-pve) Checking dmesg for errors I get the following: root@po:~# dmesg | grep -i "error" [ 4.775853] Bluetooth: HCI socket...
-
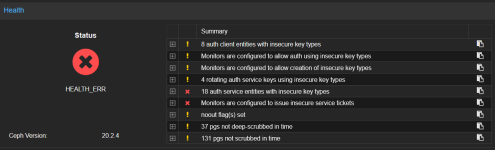
 jsterr replied to the thread PVE 9.2 + Ceph Tentacle 20.2.4: RBD operations fail because pve-storage passes removed --auth_supported option.for reference. I also used the workaround by editing the file.
-
-
 UdoB replied to the thread [SOLVED] [Virtualizing PDM] Host PVE Node Uses ZFS Storage. When installing PDM inside VM, EXT4 or ZFS?.That's interesting. Basically it's a great example of having the same information as everybody and coming to the exact opposite conclusion. While personally I would not go that road: if it works for you, it is fine! :-) (( It may depend on...
-
BBu66as replied to the thread Proxmox vollständig via Wireguard.@Supaman, einen WireGuard-Server braucht er dafür gar nicht, der PVE wird ja nur Client. Die Familie hängt schon in seinem Tunnel, also kommt auf den Host eine wg-quick-Config mit einem Peer, Endpoint auf seine Seite und PersistentKeepalive (NAT...
-
Hhuganega replied to the thread Proxmox VE 9.2 – sporadic iSCSI NOP timeouts / DID_TRANSPORT_DISRUPTED with Dell PowerVault ME5 and Intel E810.Hi Tmanok, thanks again for the suggestions. I have some new data now, so I am replacing my previous update with a more complete one. First, regarding the NIC firmware: The adapters are HPE OEM Intel E810-XXVDA2 cards. I updated both NICs from...
-
PPmUserZFS replied to the thread CEPH setup.a ACK is small, the network isnt the limiting factor for acks, its ceph "slow" architecture. [ CEPH CLIENT ] | | 1. Request Cluster Map (If needed) v [ CEPH MONITORS ] | | 2. Returns Cluster Map...
-
Jjixuuse posted the thread Manually submit spam mail and train the Bayesian filter in Mail Gateway: Installation and configuration.This small project addresses the issue discussed in https://forum.proxmox.com/threads/how-to-mark-a-delivered-email-as-spam.183728/ I would like to thank the PMG team for retaining the foundational features that make this project feasible. If...
-
JJ-Rod replied to the thread [Small Office/Home Office Deployment] Any Benefit to Combining Clustering and PDM-Based Management on Small-Scale Local Deployment?.The main advantage I see of having two PVE servers in the same cluster is that you can easily set up and manage replication between the hosts using the PVE GUI. When you need to do maintenance to one of the servers, you can hot migrate all of...
-
UdoB reacted to Bu66as's post in the thread Neuinstallation mit ZFS: verschiedene Größenangaben with
 Like.
Die Swap-Frage aus #16 ist hier irgendwie untergegangen: ja, auf die 256er ist genau richtig. Swap als zvol im rpool kann dir unter RAM-Druck den Host einfrieren (Kernel will swappen, ZFS braucht dafür selbst RAM), deshalb legt der Installer bei...
-
Ggechu posted the thread Container mount point GID mapping works, but no write access in Proxmox VE: Installation and configuration.I'm trying the new mount-point ID mapping feature introduced in Proxmox VE 9.2 with an Ubuntu 26.04 LTS unprivileged container. The host is running the latest PVE packages with kernel 7.0.14-12-pve. On the host, the shared directory is owned by...
-
JJ-Rod replied to the thread [SOLVED] [Virtualizing PDM] Host PVE Node Uses ZFS Storage. When installing PDM inside VM, EXT4 or ZFS?.TrueNAS states that they need to talk to the disks directly to be able to see the SMART data, detect and correct errors, manage scrubs and rebuilds, etc. But of course PVE has the same ZFS available, so can do all of that as well. Also, TrueNAS...
-
Einen Wireguard Server (egal ob nativ, mit OpenWRT oder OPNsene) zu konfigurieren UND das ganze in die PVE Network config einzuarbeiten ist nicht ganz trivial. Man kann alles machen, wenn man die nötigen Kenntnisse hat... das eignet mansich auch...
-
Bei Host vs. LXC noch ein Punkt: wenn WireGuard im Container läuft, hat der Host selbst gar keine WG-IP, an die sich pveproxy überhaupt binden könnte. Du müsstest den Kram dann per Routing/NAT aus dem LXC zum Host schaufeln, und die...
-
SSupaman replied to the thread Proxmox vollständig via Wireguard.Einen Wireguard Server (egal ob nativ, mit OpenWRT oder OPNsene) zu konfigurieren UND das ganze in die PVE Network config einzuarbeiten ist nicht ganz trivial. Man kann alles machen, wenn man die nötigen Kenntnisse hat... das eignet mansich auch...
-
Ddevleti posted the thread [SOLVED] Changing an Existing Subscription Key to Another Subscription Key in Proxmox VE: Installation and configuration.Hi, Could you please confirm whether my understanding below is correct? To replace an existing Proxmox subscription with another subscription key, only the subscription key needs to be updated. GUI Click Subscription on the node where you...
-
BBu66as replied to the thread Windows-VM laut PVE RAM-Verbrauch>100%.Das >100% ist der Host-RSS vom qemu-Prozess, da steckt der ganze Overhead mit drin, deshalb geht das auch mal über 100. Check mal, ob auf genau diesen VMs der QEMU-Guest-Agent läuft bzw. in den VM-Optionen überhaupt aktiviert ist (qm agent <vmid>...
-
BBei Host vs. LXC noch ein Punkt: wenn WireGuard im Container läuft, hat der Host selbst gar keine WG-IP, an die sich pveproxy überhaupt binden könnte. Du müsstest den Kram dann per Routing/NAT aus dem LXC zum Host schaufeln, und die...
-
MThere is an open bug report for this on the Debian package tracker [1] and also a proposed patch [2]. I'll keep an eye on that and hopefully remember to write here when there is an update. Best regards Jonas [1]...
-
Jjabaya91 replied to the thread Proxmox with arr stack in LXC.I know this is 2 years old but did you ever figure this out by chance? im at my wits end trying to get this to work without multiple lxc containers or moving docker to its own VM
-
TWhile researching upgrading from PVE 8 to 9, Ive read recommendations that NIC should be pinned. I see that the command was added to PVE 8. Is it as simple as running pve-network-interface-pinning generate, then rebooting?