

Hey community, we are (my company and my team) developing a ransomware safe offsite protection solution for my customers and I have made a this design to explain it:
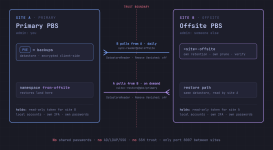
The basic principle is that we separate as much as possible. Right now I want to use TLS with firewall blocking to ensure 1-1 communication only on the API port (8007) and the encryption is there in two layers, both the encrypted backup data and the TLS "tunnel". Both sides have static IPs so that should work. If a customer does not want to expose the API port to us, then we need to add IPSec or Wireguard VPN as an option.
Here is a full blog post writeup of the concept: https://www.sbarmen.no/posts/ransomware-safe-offsite-backups-pbs/
I have this setup in my lab for now and it works perfectly. Next step is building it into our service delivery rig as a customer offering. In that offering I will also store the datastore on NFS with immutable snapshots as an option.
What do you gents think about this approach? Am I on the right track? Any suggestions?
Last edited:
