Hi
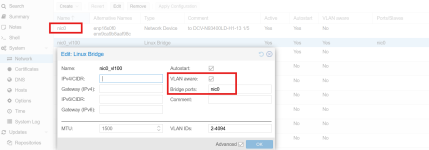
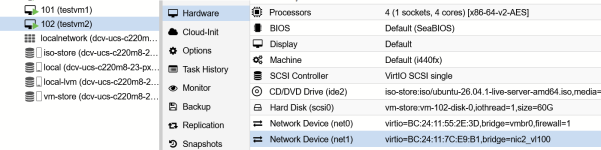
I have a problem in networking in my Proxmox v8. I use multiple VMBRs for each vlan because I want to easy selection vlan for users. When I bind vmbr450 for VM and configure network all works fine but when I want to bind vmbr0 to another VM and configure VM's network in vlan450 using vmbr0 communication doesn't work. I need use vmbr0 in particular cases and configure inside VM vlans but in this configuration PVE networking don't work fine when I use vmbr0. I want to set this up in a way that the virtual machine can receive tagged frames using vmbr0 (where the VLAN is configured internally) – something like a trunk connection. However, other virtual machines should also be able to use VLANs directly, with incoming frames being untagged by that VLAN. The end users use interfaces vmbr (i.e. vmbr450) which are connected with specified vlans. Disable or enable vlan aware it's change nothing.
Anyone could help me in my problem? Below slice of /etc/network/interfaces:
In summary, I aim to achieve a state where the interfaces consist of vmbr0, directly connected to bond0, handling all traffic, and VLAN interfaces, also associated with bond0, receiving frames with specific tags. Based on the VLAN interfaces, VMBR interfaces are created, for example, for VLAN 450, there is vmbr450.
On vm with vlan interfaces inside (when configure networking inside VM's communication doesn't work - vlan450): :

On another vm, when vmbr450 is connected directly (when configure networking inside VM's communication works fine):

Regards
Tom
I have a problem in networking in my Proxmox v8. I use multiple VMBRs for each vlan because I want to easy selection vlan for users. When I bind vmbr450 for VM and configure network all works fine but when I want to bind vmbr0 to another VM and configure VM's network in vlan450 using vmbr0 communication doesn't work. I need use vmbr0 in particular cases and configure inside VM vlans but in this configuration PVE networking don't work fine when I use vmbr0. I want to set this up in a way that the virtual machine can receive tagged frames using vmbr0 (where the VLAN is configured internally) – something like a trunk connection. However, other virtual machines should also be able to use VLANs directly, with incoming frames being untagged by that VLAN. The end users use interfaces vmbr (i.e. vmbr450) which are connected with specified vlans. Disable or enable vlan aware it's change nothing.
Anyone could help me in my problem? Below slice of /etc/network/interfaces:
Code:
auto eth6
iface eth6 inet manual
    mtu 9000

auto eth7
iface eth7 inet manual
    mtu 9000

auto bond0
iface bond0 inet manual
    bond-slaves eth6 eth7
    bond-miimon 100
    bond-mode active-backup
    bond-primary eth6
    mtu 9000

auto vmbr0
iface vmbr0 inet static
    address X.X.X.X/X
    gateway X.X.X.X
    bridge-ports bond0
    bridge-stp off
    bridge-fd 0
    bridge-vlan-aware yes
    bridge-vids 2-4094
    mtu 9000

auto vmbr450
iface vmbr450 inet manual
    bridge-ports vlan450
    bridge-stp off
    bridge-fd 0
    mtu 9000

auto vlan450
iface vlan450 inet manual
    mtu 9000
    vlan-raw-device bond0
In summary, I aim to achieve a state where the interfaces consist of vmbr0, directly connected to bond0, handling all traffic, and VLAN interfaces, also associated with bond0, receiving frames with specific tags. Based on the VLAN interfaces, VMBR interfaces are created, for example, for VLAN 450, there is vmbr450.
On vm with vlan interfaces inside (when configure networking inside VM's communication doesn't work - vlan450): :
On another vm, when vmbr450 is connected directly (when configure networking inside VM's communication works fine):
Regards
Tom
Last edited: