Latest activity
-
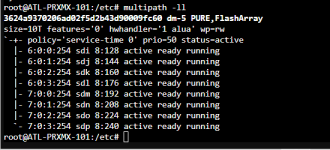
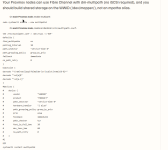
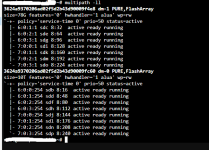
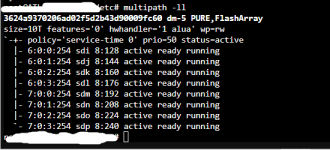
Mmarowens replied to the thread [SOLVED] Setting Up single Shared FC LUN - multipath -ll shows both Shared and boot lun.I'll take note of the screenshot issue. Thanks I installed PVE 9.2.1 on bare metal - SAN Boot obviously. When you're flying in the dark it's about seeing output change after creating the first /etc/multipath.conf file. Essentially, not...
-
JJohannes S reacted to Valombre's post in the thread Pve cluster upgrade 8.4 to 9.2 adding pve-entreprise subscription with
 Like.
Thanks all for your answers :cool:, i'll try to follow them. And if you have link/blog/posts of good how-to/experiences about qdevice configurations/state of art (made by real human) i'll be happy to read them ;) Regards.
-
JJohannes S reacted to sterzy's post in the thread Pve cluster upgrade 8.4 to 9.2 adding pve-entreprise subscription with Like.
To add to what leesteken said, you should also not rely on a cluster that is split between two different PVE versions for too long. Note that we try our best to support live migrations of guests from an older PVE version to a newer one, but not...
-
JJohannes S reacted to leesteken's post in the thread Pve cluster upgrade 8.4 to 9.2 adding pve-entreprise subscription with Like.
A good time to do that would have been when PVE 9.0/9.1/9.2 was first released and 8.4 was still in support. You are now very much behind in security updates, but which is more important (or risky) for you is eventually up to you to decide.
-
JJohannes S reacted to VictorSTS's post in the thread Pve cluster upgrade 8.4 to 9.2 adding pve-entreprise subscription with Like.
You don't specify which packages you have on PVE8 at the moment. A safe path is: Activate subscription now on PVE8. apt update && apt dist-upgrade If you already have latest packages for PVE8 from no-subscription, few or no packages will be...
-
MWondering if people starting those threads like this one here think that the Proxmox developers live under a rock...
-
 bbgeek17 replied to the thread [SOLVED] Setting Up single Shared FC LUN - multipath -ll shows both Shared and boot lun.Hi @marowens , welcome to the forum. First thing - do everyone a favor and do not use screenshots, or avoid them if at all possible. Pasting basic text and using CODE tags from the edit box menu is much easier to read. Second, did you install...
-
 the fix is in Proxmox kernels starting with pve-kernel-7.0.14-25-pve edit: as is often the case these days - the fix was picked before it got assigned a CVE (2026-10-17 vs 2016-10-23), which is why the CVE is not included in the git or package...
-
Mmarowens posted the thread [SOLVED] Setting Up single Shared FC LUN - multipath -ll shows both Shared and boot lun in Proxmox VE: Installation and configuration.I'm setting up a test proxmox lab. It's been a minute but what was new this time was I'm using block level LUNs from a Pure Flash Array. My UCS blades do not have local storage so my service profile was setup properly to access the Pure Array...
-
-
Mmlazarin reacted to Wielder3763's post in the thread Cannot mount CephFS filesystems on VMs or external systems after upgrading to Ceph 20.2.4 with Like.
I ran into this same issue while updating my Proxmox Ceph cluster and migrating to the new aes256k authentication keys. I actually developed a lightweight replacement for mount.ceph some time ago for a completely different reason. I use Arch...
-
SSpacemanSpiff posted the thread Mouse not aligned with SPICE display. in Proxmox VE: Installation and configuration.Hey all, I'm running into a new issue with a new Windows Server 2025 VM running on my Proxmox cluster. I enabled the SPICE display and SPICE enhancements in the VM settings and I've installed the virtIO tools which included the QEMU Guest Tools...
-
 SteveITS replied to the thread Pve cluster upgrade 8.4 to 9.2 adding pve-entreprise subscription.It’s actually quite easy, install the packages and run the command. https://pve.proxmox.com/pve-docs/chapter-pvecm.html#_corosync_external_vote_support Most of that describes how/why it is used. Note you must remove it before adding or...
-
VValombre replied to the thread Pve cluster upgrade 8.4 to 9.2 adding pve-entreprise subscription.Thanks all for your answers :cool:, i'll try to follow them. And if you have link/blog/posts of good how-to/experiences about qdevice configurations/state of art (made by real human) i'll be happy to read them ;) Regards.
-
SSpacemanSpiff reacted to UdoB's post in the thread Modify existing fresh install or just reinstall to add ceph? with Like.
No, there is no need to do that. Just follow the docs to add the ceph-repository. Then you can install the whole shebang - includings OSDs, MONs and MGRs - from the web gui. (Just for reference: the official docs are there...
-
Kkawano-y replied to the thread Proxmox stuck on grub after reboot.Hi, Could you share the exact GRUB error message or a photo of the screen? Also, could you clarify which disk and partitions you created or modified before rebooting?
-
Ttakt reacted to MDSOperator's post in the thread Proxmox VE 7 is vulnerable to some type of 0day/RCE non auth with Like.
Proxmox VE 7.1 - cryptojacking rootkit + root SSH backdoor: full teardown TL;DR Two PVE 7 hosts were compromised and running an XMRig cryptominer hidden by a preload rootkit. The same "install_and_mine.sh / libhide" toolchain planted: A...
-
JJohannes S reacted to Bu66as's post in the thread [SOLVED] Ceph S3 Storage und Veeam M365 Backup with Like.
Das liegt dann an Veeam. Laut SigV4-Spec muss content-type mit in die CanonicalHeaders, wenn der Header im Request steckt. Veeam schickt ihn mit, signiert ihn aber nicht, und RGW lehnt das korrekt ab. Würd ein Ticket bei Veeam aufmachen und die...
-
JJohannes S reacted to Ingo S's post in the thread [SOLVED] Ceph S3 Storage und Veeam M365 Backup with Like.
Okay okay ich glaube ich habe eine heiße Spur: Ich hatte vergessen, dass wir für HA über einen HAProxy im Round Robin auf zwei verschiedenen Servern mit dem Cluster kommunizieren und der Fehler vielleicht deshalb nicht im Log drinne ist. Habe...
-
JJohannes S reacted to Ingo S's post in the thread [SOLVED] Ceph S3 Storage und Veeam M365 Backup with Like.
Oi... yikes, warum finde eigentlich immer ICH solche Bugs :rolleyes::D Danke dir! Da der HAProxy im TCP Mode läuft wird das leider nichts mit dem Entfernen des Header. Dann mache ich mal ein Ticket bei veeam auf. (Ich wette, wenn ich statt "S3...
-
JJohannes S reacted to Ingo S's post in the thread [SOLVED] Ceph S3 Storage und Veeam M365 Backup with Like.
Update: Die Ursache dieser ganzen Misere ist ein Fix für CVE-2026-54330 der die SigV4 zu strikt auslegt um die Schwachstelle zu schließen. Die Regression wird mit dem Release 20.2.5, das gestern angekündigt wurde, behoben ->...