Latest activity
-
JJohannes S reacted to BobhWasatch's post in the thread Proxmox VE 7 is vulnerable to some type of 0day/RCE non auth with
 Like.
Only to you, unless you are claiming that it affects an up-to-date version of PVE. PVE 7 is based on Debian 11, PVE 8 on Debian 12. So they would be affected by that bug unless they were updated since the bug was fixed.
-
JJohannes S reacted to Gilberto Ferreira's post in the thread Proxmox VE 7 is vulnerable to some type of 0day/RCE non auth with Like.
In any case, I don't think this is a 0day vulnerability, because on this is happen due to out date servers and bad servers administration, to say the least. Many of this vulnerabilities are well-know documented, such as kernel and ssh...
-
JJohannes S reacted to leesteken's post in the thread Proxmox VE 7 is vulnerable to some type of 0day/RCE non auth with Like.
Search for 8. in these posts here: https://forum.proxmox.com/threads/proxmox-virtual-environment-security-advisories.149331/ . PVE 8 is also vulnerable to lots of things unless completely up to date but it most likely does not get any updates...
-
JJohannes S reacted to JensF's post in the thread Proxmox VE 7 is vulnerable to some type of 0day/RCE non auth with Like.
PVE 8 is EOL too. Even if it's not affected this time, Kernel vulnerabilities are found almost every week. It's just a matter of time.
-
SSchorschSK reacted to nodoame's post in the thread High VM-EXIT and Host CPU usage on idle with Windows Server 2025 with Like.
I can confirm EnablePerCpuClockTickScheduling=2 fixes / works around the issue. CPU load returns to 23H2 levels and CPU cores assigned to the VM are able to enter deeper C states as expected. Thank you! I've attached this info to the QEMU ticket...
-
Uurog replied to the thread Proxmox VE 7 is vulnerable to some type of 0day/RCE non auth.I also have a Proxmox 7 with the same problem and screenshots that have already been posted.
-
Ggfngfn256 replied to the thread Proxmox VE 7 is vulnerable to some type of 0day/RCE non auth.Not sure what you mean by "Everything". So far you only reported your own single host being attacked. Are you (by chance) connected to arjitc, the other reporter of this attack. (Interestingly both these users only joined today, for the purpose...
-
BBobhWasatch replied to the thread Proxmox VE 7 is vulnerable to some type of 0day/RCE non auth.Only to you, unless you are claiming that it affects an up-to-date version of PVE. PVE 7 is based on Debian 11, PVE 8 on Debian 12. So they would be affected by that bug unless they were updated since the bug was fixed.
-
 UdoB reacted to Bu66as's post in the thread OT: Debian erlaubt KI-Beiträge ohne Kennzeichnungspflicht with Like.
Ehrlich gesagt ändert das bei Debian doch wenig, mit dem DCO lag die Verantwortung schon immer beim Einreicher. Ungeprüft zusammenkopierten Kram gab's auch vorher schon, halt von Stack Overflow statt vom LLM. Was real schützt ist der Review- und...
-
Ppve7bug replied to the thread Proxmox VE 7 is vulnerable to some type of 0day/RCE non auth.Everything happened on the same day at the same time. Of course, it's a zero-day vulnerability and affects several versions of Proxmox. Exposing Proxmox to the internet doesn't make it hackable with a single click. There are no publicly available...
-
Ggfngfn256 reacted to Neobin's post in the thread Proxmox VE 7 is vulnerable to some type of 0day/RCE non auth with Like.
So, you are: Running a OS that is EOL since two years Exposing it to the internet Disabling the firewall If this is not a troll, I hope the lesson was learned...
-
GGilberto Ferreira replied to the thread Proxmox VE 7 is vulnerable to some type of 0day/RCE non auth.In any case, I don't think this is a 0day vulnerability, because on this is happen due to out date servers and bad servers administration, to say the least. Many of this vulnerabilities are well-know documented, such as kernel and ssh...
-
IIsThisThingOn reacted to gurubert's post in the thread Proxmox VE 7 is vulnerable to some type of 0day/RCE non auth with Like.
Sorry for your loss, but why would anyone do that?
-
CCarlos Gomes reacted to Gilberto Ferreira's post in the thread Proxmox VE 7 is vulnerable to some type of 0day/RCE non auth with Like.
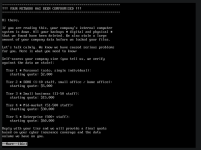
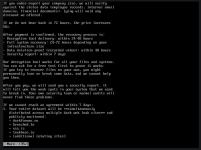
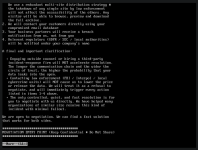
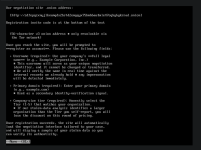
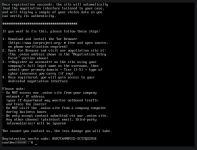
I got reports from Proxmox VE 8.0.3, 8.2 and 8.4 as well... And here is a compromissed server:
-
Ppve7bug replied to the thread Proxmox VE 7 is vulnerable to some type of 0day/RCE non auth.I got the same message on my Proxmox VE 7.
-
GGilberto Ferreira replied to the thread Proxmox VE 7 is vulnerable to some type of 0day/RCE non auth.I got reports from Proxmox VE 8.0.3, 8.2 and 8.4 as well... And here is a compromissed server:
-
-
BBu66as replied to the thread OT: Debian erlaubt KI-Beiträge ohne Kennzeichnungspflicht.Ehrlich gesagt ändert das bei Debian doch wenig, mit dem DCO lag die Verantwortung schon immer beim Einreicher. Ungeprüft zusammenkopierten Kram gab's auch vorher schon, halt von Stack Overflow statt vom LLM. Was real schützt ist der Review- und...
-
Eesnmb replied to the thread High Availability Functionality.Ha, this is exactly it. Thanks!
-
Jjoel0 reacted to markVnl's post in the thread Testing Proxmox VE on Ampere Altra Max (Armv8) with Like.
Thank you, very very much!! I've been chasing the cause these crashes on debian-arm64 with qemu and graphical consoles for a long time now. This sorts it out.
-
GGilberto Ferreira reacted to leesteken's post in the thread Proxmox VE 7 is vulnerable to some type of 0day/RCE non auth with Like.
Search for 8. in these posts here: https://forum.proxmox.com/threads/proxmox-virtual-environment-security-advisories.149331/ . PVE 8 is also vulnerable to lots of things unless completely up to date but it most likely does not get any updates...