Latest activity
-
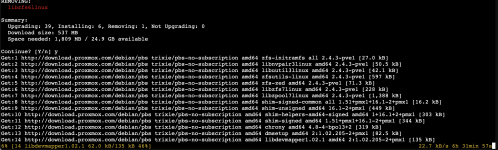
TTmanok posted the thread Horrifically slow download speeds for download.proxmox.com? in Proxmox VE: Networking and Firewall.Hi Everyone, Hey PVE Staff, Is it just me, or are the web servers for download.proxmox.com unbelievably slow? I'm updating a PBS instance after several months and realizing it will take hours.... This is naturally, inconveniently interfering...
-
-
PPikachuEXE replied to the thread OPNSense cannot get WAN IP via DHCP from ISP on host boot.Running DHCP on host works though via `dhclient -d nic3` (before I restart `nic3` But even I suspect it's the bridge or whatever blocking the DHCP request, I still got no idea via `tcpdump` (still see DHCP requests I also never see DISCOVER from...
-
Ccyberming posted the thread Missing `ifupdown2` 3.0.0-1.3 for ARM64 in Trixie `pve-no-subscription` repo in Proxmox VE: Installation and configuration.Hello everyone, This is my first post. I am trying to install Proxmox VE on Debian 13 (Trixie) on an ARM64 (aarch64) system. But I wanted to report a missing package that causes the update network configuration to fail. **Issue:** The...
-
JJ-Rod replied to the thread Very specific setup, needing very specific advisory.I'm not sure why you are stipulating no additional VMs. I think it makes the most sense to me for PVE to consume the storage first since it has a decent list of local redundant storage options. Then everything is a VM on top of that. That is...
-
JJ-Rod replied to the thread Has anyone tried Ubiquiti's ENAS for ProxMox's storage array?.How are you making the storage HA? Or are you not storing the OS virtual disks on the NAS and it's just for bulk storage?
-
TTmanok replied to the thread Proxmox VE 9.2 – sporadic iSCSI NOP timeouts / DID_TRANSPORT_DISRUPTED with Dell PowerVault ME5 and Intel E810.Hi Huganega, Ok, a few things from your output might be worth examining, but I have to ask a question I normally ignore because I'm vendor agnostic 99% of the time. Are you using a Dell recommended DAC? 25GbE has caused me trouble in the past...
-
PPmUserZFS replied to the thread CEPH setup.# ceph osd tree ID CLASS WEIGHT TYPE NAME STATUS REWEIGHT PRI-AFF -1 18.14612 root default -3 3.02435 host pm1 0 sas 0.75609 osd.0...
-
JAch? Da erkennst du keine leichte Paranoia? Jedes segmentierte Netzwerk setzt auf Layer3. Sonst wird es schwierig, sich zu "verstecken" oder Datenverkehr funktioniert einfach nicht. Layer-2 wirst du inzwischen selbst beim DE-CIX mit der Lupe...
-
JIch weiß nicht, wie weit ein IDS gegen Bedrohungen hilft, die noch gar nicht klassifiziert sind. Die Verbindung zur Hersteller-Cloud mag es sehen, aber nicht notwendigerweise als bösartig erkennen. Und den anschließenden Layer-2-Traffic innerhalb...
-
PPmUserZFS replied to the thread CEPH setup.Old cluster (4K write)New vm-hot (4K write)Improvement Avg latency2.49ms1.52ms~39% lower Avg IOPS6,41510,504~64% higher Max latency (tail)65.7ms7.55ms~8.7x lower
-
JOh, viele. Praktisch jedes cloudbasierte IoT-Endgerät kann potentiell als Einfallstor genutzt werden, da jede bestehende Verbindung in beiden Rcihtungen genutzt werden kann. Wird der Hersteller gehackt (oder hatte er sowieso böse Absichten)...
-
JJohannes S replied to the thread Proxmox vollständig via Wireguard.Was ist daran einfach, wenn eine Fehlkonfiguration von wireguard die Netzwerkkonfiguration des Hosts zerschießen kann?
-
JUm eine LARA anzustöpseln, muss ich als böser Bube nur einen MA bei Hetzner glaubhaft machen, dass der bin für den ich mich ausgebe. Das ist sicherheitstechnisch linke vs. rechte Tasche. Echt sicher, bedeutet einen administrativen Alptraum von...
-
JWarum so ein Aufriss, wenn ich einfach nur TOTP aktivieren kann?
-
JOder per Konsole. Auf die hat die Familie ja Zugriff. Bei Hetzner mache ich das entweder über eine Lara (oder indem ich eine "versteckte" IPv6 für Proxmox auf vmbr0 nutze - die kann man ja per Portscan kaum finden).
-
JJohannes S reacted to Kingneutron's post in the thread ZFS dedup on a Proxmox host in 2026 — has fast dedup changed the recommendation? with
 Like.
It doesn't, really. Live dedup is just the way it came out as implemented in the original Solaris code. PBS does after-the-fact dedup on filesystems other than ZFS. It gets run by the garbage-collection job...
-
JJohannes S reacted to Kingneutron's post in the thread ZFS dedup on a Proxmox host in 2026 — has fast dedup changed the recommendation? with Like.
I'll try to post something later tonight or this weekend, after the primetime electric rates go down...
-
Jjeenam replied to the thread [TUTORIAL] HOWTO - Proxmox VE 8-x.x Wifi with routed configuration.This Tutorial also works for Proxmox v9.x.
-
TTErxleben replied to the thread Proxmox vollständig via Wireguard.Ach? Da erkennst du keine leichte Paranoia? Jedes segmentierte Netzwerk setzt auf Layer3. Sonst wird es schwierig, sich zu "verstecken" oder Datenverkehr funktioniert einfach nicht. Layer-2 wirst du inzwischen selbst beim DE-CIX mit der Lupe...
-
Mmeyergru replied to the thread Proxmox vollständig via Wireguard.Ich weiß nicht, wie weit ein IDS gegen Bedrohungen hilft, die noch gar nicht klassifiziert sind. Die Verbindung zur Hersteller-Cloud mag es sehen, aber nicht notwendigerweise als bösartig erkennen. Und den anschließenden Layer-2-Traffic innerhalb...