Hello,
I am running Proxmox Mail Gateway 9.1.0 with two network interfaces:
ens192 public-address.240/24
ens224 192.168.10.240/24
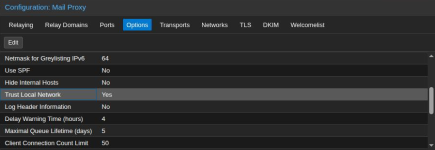
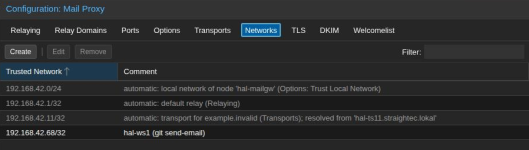
Under Configuration > Mail Proxy > Networks, I configured only explicit /32 trusted hosts. The public /24 subnet is not displayed in the GUI and is not present in /etc/pmg/mynetworks.
However, the generated Postfix configuration contains the entire directly connected public subnet:
The subnet appears to be derived automatically from the PMG interface configuration.
I understand that this is currently documented behavior and that directly connected networks are automatically trusted for the internal SMTP port. I also understand that it can be overridden by maintaining a custom /etc/pmg/templates/main.cf.in.
However, the effective trusted subnet is not visible in the PMG GUI. An administrator reviewing Configuration > Mail Proxy > Networks may therefore assume that only the explicitly listed /32 hosts are trusted.
Could PMG provide the following options?
Is there currently a supported PMG 9 method to disable the automatically added subnet while continuing to manage explicit trusted hosts through the GUI?
Thank you.
I am running Proxmox Mail Gateway 9.1.0 with two network interfaces:
ens192 public-address.240/24
ens224 192.168.10.240/24
Under Configuration > Mail Proxy > Networks, I configured only explicit /32 trusted hosts. The public /24 subnet is not displayed in the GUI and is not present in /etc/pmg/mynetworks.
However, the generated Postfix configuration contains the entire directly connected public subnet:
Code:
postfix.mynetworks = 127.0.0.0/8 192.168.10.250/32 ... public-address.0/24 ... [::1]/128I understand that this is currently documented behavior and that directly connected networks are automatically trusted for the internal SMTP port. I also understand that it can be overridden by maintaining a custom /etc/pmg/templates/main.cf.in.
However, the effective trusted subnet is not visible in the PMG GUI. An administrator reviewing Configuration > Mail Proxy > Networks may therefore assume that only the explicitly listed /32 hosts are trusted.
Could PMG provide the following options?
- Display automatically generated trusted networks in the GUI as read-only entries.
- Add an option to disable automatic trust of directly connected subnets.
- Allow administrators to use only explicitly configured trusted hosts without overriding the complete main.cf.in template.
- Show a warning when the internal SMTP port is reachable through a public-addressed interface.
Is there currently a supported PMG 9 method to disable the automatically added subnet while continuing to manage explicit trusted hosts through the GUI?
Thank you.